Tuesday, June 9, 2015

Network Security Attacks and Defence

Network security

Network security involves the authorization of access to data in a network, which is controlled by the network administrator. Users choose or are assigned an ID and password or other authenticating information that allows them access to information and programs within their authority. Network security covers a variety of computer networks, both public and private, that are used in everyday jobs conducting transactions and communications among businesses, government agencies and individuals. Networks can be private, such as within a company, and others which might be open to public access. Network security is involved in organizations, enterprises, and other types of institutions. It does as its title explains: It secures the network, as well as protecting and overseeing operations being done. The most common and simple way of protecting a network resource is by assigning it a unique name and a corresponding password.


Types of attacks include:


Active

      1.  Denial-of-service attack (DoS)

      2.  Spoofing

      3.  Man in the middle

      4.  ARP poisoning
      5.  DNS Spoofing

      6.  Smurf attack

      7.  Buffer overflow

      8.  Heap overflow

      9.  Format string attack

      10.  SQL injection
      11. Cyber attack

 Passive
      1. Network

             a. Wiretapping

             b. Port scanner

             c. Idle scan
 

Denial-of-Service Attack (DoS)

 Denial of Service (DoS) attacks are among the most feared threats in today's cybersecurity landscape. Difficult to defend against and potentially costly, DoS attacks can cause outages of web sites and network services for organizations large and small. DoS attacks can also be lucrative for criminals, some of whom use these attacks to shake down businesses for anywhere from thousands to millions of dollars. 

DoS attack is used as a distraction to funnel attention and resources away while a targeted breach attack is being launched. Anonymous used that technique in a major 2011 attack that ultimately led to the theft of over 12 million customers' credit card data.


 DoS vs DDoS


The most easily executed type of DoS attack is one that is launched from a single origin. In this attack, a single machine somewhere on the Internet issues a barrage of network requests against a targeted victim machine. The requests themselves can take a variety of forms – for example, an  attack might use ICMP Flooding via ping requests, or HTTP requests against a web server.

In a DDoS attack, the incoming traffic flooding the victim originates from many different sources – potentially hundreds of thousands or more. This effectively makes it impossible to stop the attack simply by blocking a single IP address; plus, it is very difficult to distinguish legitimate user traffic from attack traffic when spread across so many points of origin.

How a Denial of Service Attack Works

The simple approach to DOS is to flood a server with a large amount of pointless traffic. This gives the server far too much to deal with. Bandwidth escalates, memory is exhausted and ordinary users can’t get a connection to the server.
But actually maxing out a server can be quite difficult, even with a large number of computers opening up as many connections as they can. As such, attackers have come up with a way to magnify the effect by using fake IP addresses.
Using fake IPs, the same process can be carried out by one computer, a botnet that’s controlled by one master or, as with Operation Payback, a group of people working together.
Here’s what happens.

  1. The attacking machine sends a SYN packet to the server. However, it makes it appear to come from somewhere else.
  2. The server then responds with a SYN/ACK packet, but there’s no response – the sender address was fake.
  3. The server continues to wait for a reply, keeping the connection open and in its memory until it times out.
The server keeps a bunch of useless connections open, losing more and more memory to the attack and eventually becoming crippled.
The strategy is actually fairly successful. It has slowed or crashed some prominent sites.
However, companies have become wise to DDOS attacks and have begun to take some precautions.

Risks Associated with Denial of Service Attacks

Denial of Service attacks are centered around the concept that by overloading a target’s resources, the system will ultimately crash. In the case of a DoS attack against a web application, the software is overloaded by the attack and the application fails to serve web pages properly. To crash a web server running an application, a DoS threat attacks the following services:

  • Network bandwidth
  • Server memory
  • Application exception handling mechanism
  • CPU usage
  • Hard disk space
  • Database space
  • Database connection pool

Can a DDoS be stopped ?

Let's start with the bad news: It is very difficult to defend against a sophisticated DDoS attack launched by a determined adversary.

There are several ways to defend against a DDOS attack. None can guarantee prevention, but the website owner does have options:

  1. Filtering: Routers at the edge of the network can be trained to spot and drop DDOS connections, preventing them from slowing the network or the server.
  2. Moving: If the attack is pointed at a specific IP address, the site’s IP can be changed. This is what the White House did before a nasty computer virus tried to DDOS its site.
  3. Blackholing: A host may simply “blackhole” a site that is being DDOSed, directing all traffic to it to an address that doesn’t exist. This is normally a last resort.
In addition, many companies sell anti-DDOS applications that detect and block attacks.
The only sure-fire way to end a DDOS attack is to wait it out. Most attacks don’t last very long because those with botnets don’t wish to expose their network for too long, and group attacks can’t hold their cohesion forever. Though it may take a few days, the attack will cease of its own accord.
 

Spoofing

A spoofing attack is when a malicious party impersonates another device or user on a network in order to launch attacks against network hosts, steal data, spread maleware or bypass access controls. There are several different types of spoofing attacks that malicious parties can use to accomplish this. Some of the most common methods include IP address spoofing attacks, ARP spoofing attacks and DNS server spoofing attacks.


ARP Spoofing/ Poisoning

 ARP Spoofing/ Poisoning is a technique whereby an attacker sends fake ("spoofed") Address Resolution Protocol (ARP) messages onto a Local Area Network. Generally, the aim is to associate the attacker's MAC address with the IP address of another host (such as the default gateway), causing any traffic meant for that IP address to be sent to the attacker instead.

ARP spoofing may allow an attacker to intercept data frames on a LAN, modify the traffic, or stop the traffic altogether. Often the attack is used as an opening for other attacks, such as denial of service, man in the middle, or session hijacking attacks.
The attack can only be used on networks that make use of the Address Resolution Protocol (ARP), and is limited to local network segments.


DNS Server Spoofing Attacks

The Domain Name System (DNS) is a system that associates domain names with IP addresses. Devices that connect to the internet or other private networks rely on the DNS for resolving URLs, email addresses and other human-readable domain names into their corresponding IP addresses. In a DNS server spoofing attack, a malicious party modifies the DNS server in order to reroute a specific domain name to a different IP address. In many cases, the new IP address will be for a server that is actually controlled by the attacker and contains files infected with malware. DNS server spoofing attacks are often used to spread computer worms and viruses.

Spoofing Attack Prevention and Mitigation

There are many tools and practices that organizations can employ to reduce the threat of spoofing attacks. Common measures that organizations can take for spoofing attack prevention include:

  • Packet filtering: Packet filters inspect packets as they are transmitted across a network. Packet filters are useful in IP address spoofing attack prevention because they are capable of filtering out and blocking packets with conflicting source address information (packets from outside the network that show source addresses from inside the network and vice-versa).
  • Avoid trust relationships: Organizations should develop protocols that rely on trust relationships as little as possible. It is significantly easier for attackers to run spoofing attacks when trust relationships are in place because trust relationships only use IP addresses for authentication.
  • Use spoofing detection software: There are many programs available that help organizations detect spoofing attacks, particularly ARP spoofing. These programs work by inspecting and certifying data before it is transmitted and blocking data that appears to be spoofed.
  • Use cryptographic network protocols: Transport Layer Security (TLS), Secure Shell (SSH), HTTP Secure (HTTPS) and other secure communications protocols bolster spoofing attack prevention efforts by encrypting data before it is sent and authenticating data as it is received.


Man in the Middle

In cryptography and computer security, the man-in-the-middle attack (often abbreviated to MITM, MitM, MIM, MiM or MITMA) requires an attacker to have the ability to both monitor and alter or inject messages into a communication channel. One example is active eavesdropping, in which the attacker makes independent connections with the victims and relays messages between them to make them believe they are talking directly to each other over a private connection, when in fact the entire conversation is controlled by the attacker. The attacker must be able to intercept all relevant messages passing between the two victims and inject new ones. This is straightforward in many circumstances; for example, an attacker within reception range of an unencrypted Wi-Fi wireless access point, can insert himself as a man-in-the-middle.


 As an attack that aims at circumventing mutual authentication, or lack thereof, a man-in-the-middle attack can succeed only when the attacker can impersonate each endpoint to their satisfaction as expected from the legitimate other end. Most cryptographic protocols include some form of endpoint authentication specifically to prevent MITM attacks. For example, TLS can authenticate one or both parties using a mutually trusted certification authority.

Smurf Attack

 The Smurf Attack is a distributed denial-of-service attack in which large numbers of Internet Control Message Protocol (ICMP) packets with the intended victim's spoofed source IP are broadcast to a computer network using an IP Broadcast address. Most devices on a network will, by default, respond to this by sending a reply to the source IP address. If the number of machines on the network that receive and respond to these packets is very large, the victim's computer will be flooded with traffic. This can slow down the victim's computer to the point where it becomes impossible to work on.


 Buffer Overflow

 In computer security and programming, a buffer overflow, or buffer overrun, is an anomaly where a program, while writing data to a buffer, overruns the buffer's boundary and overwrites adjacent memory. This is a special case of violation of memory safety.
Buffer overflows can be triggered by inputs that are designed to execute code, or alter the way the program operates. This may result in erratic program behavior, including memory access errors, incorrect results, a crash, or a breach of system security. Thus, they are the basis of many software vulnerabilities and can be maliciously exploited.


 Programming languages commonly associated with buffer overflows include C and C++, which provide no built-in protection against accessing or overwriting data in any part of memory and do not automatically check that data written to an array (the built-in buffer type) is within the boundaries of that array. Bounds checking can prevent buffer overflows.

Exploitation


  1. Stack-based exploitation
  2. Heap-based exploitation
  3. Barriers to exploitation
  4. Practicalities of exploitation
         => NOP sled technique,
         => The jump to address stored in a register technique


Protective Countermeasures


  1. Choice of programming language
  2. Use of safe libraries
  3. Buffer overflow protection
  4. Pointer protection
  5. Executable space protection
  6. Address space layout randomization
  7. Deep packet inspection

 Heap Overflow 

 A heap overflow is a type of buffer overflow that occurs in the heap data area. Heap overflows are exploitable in a different manner to that of stack-based overflows. Memory on the heap is dynamically allocated by the application at run-time and typically contains program data. Exploitation is performed by corrupting this data in specific ways to cause the application to overwrite internal structures such as linked list pointers. The canonical heap overflow technique overwrites dynamic memory allocation linkage (such as malloc meta data) and uses the resulting pointer exchange to overwrite a program function pointer.


Format String Attack

Uncontrolled format string is a type of software vulnerability, discovered around 1999, that can be used in security exploits. Previously thought harmless, format string exploits can be used to crash a program or to execute harmful code. The problem stems from the use of unchecked user input as the format string parameter in certain C functions that perform formatting, such as “printf()”. A malicious user may use the “%s”  & “%x” format tokens, among others, to print data from the stack or possibly other locations in memory. One may also write arbitrary data to arbitrary locations using the “%n” format token, which commands “printf()” and similar functions to write the number of bytes formatted to an address stored on the stack.

SQL Injection

SQL injection is a code injection technique, used to attack data-driven applications, in which malicious SQL statements are inserted into an entry field for execution (e.g. to dump the database contents to the attacker). SQL injection must exploit a security vulnerability in an application's software, for example, when user input is either incorrectly filtered for string literal escape characters embedded in SQL statements or user input is not strongly typed and unexpectedly executed. SQL injection is mostly known as an attack vector for websites but can be used to attack any type of SQL database.

In a 2012 study, security company Imperva observed that the average web application received 4 attack campaigns per month, and retailers received twice as many attacks as other industries.

Technical Implementations


  1. Incorrectly filtered escape characters
  2. Incorrect type handling
  3. Blind SQL injection
  4. Conditional responses
  5. Second Order SQL Injection

Mitigation


  1. Parameterized statements
  2. Enforcement at the coding level
  3. Escaping
  4. Pattern check
  5. Database permissions

 Cyber Attack

Cyber-attack is any type of offensive maneuver employed by individuals or whole organizations that targets computer information systems, infrastructures, computer networks, and/or personal computer devices by various means of malicious acts usually originating from an anonymous source that either steals, alters, or destroys a specified target by hacking into a susceptible system. These can be labelled as either a Cyber campaign, cyber-warfare or cyber-terrorism in different context. Cyber-attacks can range from installing spyware on a PC to attempts to destroy the infrastructure of entire nations. Cyber-attacks have become increasingly sophisticated and dangerous as the Stuxnet worm recently demonstrated.


 cyber attack prevention

  • Never click on links in emails. If you do think the email is legitimate, whether from a third party retailer or primary retailer, go to the site and log on directly. Whatever notification or service offering was referenced in the email, if valid, will be available via regular log on.
  • Never open the attachments. Typically, retailers will not send emails with attachments. If there is any doubt, contact the retailer directly and ask whether the email with the attachment was sent from them.
  • Do not give out personal information over the phone or in an email unless completely sure. Social engineering is a process of deceiving individuals into providing personal information to seemingly trusted agents who turn out to be malicious actors. If contacted over the phone by someone claiming to be a retailer or collection agency, do not give out your personal information. Ask them to provide you their name and a call-back number. Just because they may have some of your information does not mean they are legitimate!
Other practical tips to protect yourself from cyber attacks:
  • Set secure passwords and don't share them with anyone. Avoid using common words, phrases, or personal information and update regularly.
  • Keep your operating system, browser, anti-virus and other critical software up to date. Security updates and patches are available for free from major companies.
  • Verify the authenticity of requests from companies or individuals by contacting them directly. If you are asked to provide personal information via email, you can independently contact the company directly to verify this request.
  • Pay close attention to website URLs. Pay attention to the URLs of websites you visit. Malicious websites sometimes use a variation in common spelling or a different domain (for example, .com instead of .net) to deceive unsuspecting computer users.
  • For e-Mail, turn off the option to automatically download attachments.
  • Be suspicious of unknown links or requests sent through email or text message. Do not click on unknown links or answer strange questions sent to your mobile device, regardless of who the sender appears to be.

Wiretapping

Telephone tapping (also wire tapping or wiretapping in American English) is the monitoring of telephone and Internet conversations by a third party, often by covert means. The wire tap received its name because, historically, the monitoring connection was an actual electrical tap on the telephone line. Legal wiretapping by a government agency is also called lawful interception. Passive wiretapping monitors or records the traffic, while active wiretapping alters or otherwise affects it.  


 Port scanner

A port scanner is a software application designed to probe a server or host for open ports. This is often used by administrators to verify security policies of their networks and by attackers to identify running services on a host with the view to compromise it.

A port scan or port scan can be defined as a process that sends client requests to a range of server port addresses on a host, with the goal of finding an active port. While not a nefarious process in and of itself, it is one used by hackers to probe target machine services with the aim of exploiting a known vulnerability of that service. However the majority of uses of a port scan are not attacks and are simple probes to determine services available on a remote machine.


To portsweep is to scan multiple hosts for a specific listening port. The latter is typically used to search for a specific service, for example, an SQL-based computer worm may portsweep looking for hosts listening on TCP port 1433.


Types

  1. TCP scanning
  2. SYN scanning
  3. UDP scanning
  4. ACK scanning
  5. Window scanning
  6. FIN scanning
  7. Other scan types

 Idle Scan

The idle scan is a TCP port scan method that consists of sending spoofed packets to a computer to find out what services are available. This is accomplished by impersonating another computer called a "zombie" (that is not transmitting or receiving information) and observing the behavior of the ''zombie'' system.


Overall Defense against Network Attack

Configuration Management


The main weapon in network attack defense is tight configuration management. The following measures should be strictly implemented as part of configuration management.

• If the machines in your network should be running up-to-date copies of the operating system and they are immediately updated whenever a new service pack or patch is released.

• All your configuration files in your Operating Systems or Applications should have enough security.

• All the default passwords in your Operating Systems or Applications should be changed after the installation.

• You should implement tight security for root/Administrator passwords.
 

Firewalls


Another weapon for defense against network attack is Firewall. Firewall is a device and/or a sotware that stands between a local network and the Internet, and filters traffic that might be harmful. Firewalls can be classified in to four based on whether they filter at the IP packet level, at the TCP session level, at the application level or hybrid.

1. Packet Filtering: Packet filtering firewalls are functioning at the IP packet level. Packet filtering firewalls filters packets based on addresses and port number. Packet filtering firewalls can be used as a weapon in network attack defense against Denial of Service (DoS) attacks and IP Spoofing attacks.

2. Circuit Gateways: Circuit gateways firewalls operate at the transport layer, which means that they can reassemble, examine or block all the packets in a TCP or UDP connection. Circuit gateway firewalls can also Virtual Private Network (VPN) over the Internet by doing encryption from firewall to firewall.

3. Application Proxies: Application proxy-based firewalls function at the application level. At this level, you can block or control traffic generated by applications. Application Proxies can provide very comprehensive protection against a wide range of threats.

4. Hybrid: A hybrid firewall may consist of a pocket filtering combined with an application proxy firewall, or a circuit gateway combined with an application proxy firewall.
 

Encryption


Encryption is another great weapon used in defense against network attacks. Click the following link to get a basic idea of encryption.

Encryption can provide protection against eavesdropping and sniffer attacks. Private Key Infrastructure (PKI) Technologies, Internet Protocol Security (IPSec), and Virtual Private Networks (VPN) when implemented properly, can secure you network against network attacks.

Other tips for defense against network attack are

• Privilege escalation at different levels and strict password policies

• Tight physical security for all your machines, especially servers.

• Tight physical security and isolation for your back up data.

Saturday, June 6, 2015

Cisco ASA Firewall Setup Wizard

Cisco ASA

ASA in Cisco ASA stands for Adaptive Security Appliance.

In brief, Cisco ASA is a  security device that combines firewall, antivirus, intrusion prevention, and virtual private network (VPN) capabilities.  It provides proactive threat defense that stops attacks before they spread through the network. Indeed, it's the whole package, so to speak.

An ASA is valuable and flexible in that it can be used as a security solution for both small and large networks.
Beyond being a firewall, the Cisco ASA can do the following and more:
  • antivirus

  • antispam

  • IDS/IPS engine

  • VPN device

  • SSL device

  • content inspection


Cisco ASA Set-up Wizard

After you are connected to your Cisco ASA Firewall, you'll have to decide whether to use the startup wizard or use a different configuration methods. The introduction page will appear and which allows you to make a decision. Because you need to have Java installed on your PC.
you have three choices here:
  • Install ASDM Launcher and Run Cisco Adaptive Security Device Manager (ASDM): Installs the ASDM on your computer. If this is the computer you will always use to perform your management, this method makes the most sense.
  • Run ASDM: This option uses Java Web Start to launch the ASDM tool directly from the copy installed on the ASA. This is beneficial if you are not at your normal computer because you do not install any software.
  • Run Start-up Wizard: This option also uses Java Web Start to launch ASDM, with one exception; after the ASDM has launched, the Start-up Wizard runs automatically.


To perform the network configuration of the ASA, the following process walks you through the Startup Wizard:
  1. Click the Run Start-up Wizard button on the introduction page.

    You receive a warning related to the security settings on Java.

  2. If you are sure that you are connected to the correct device on the network and not some fake device trying to collect your credentials, dismiss the warning message.

    Because you expect this message from the ASDM, continue to the website. The Cisco ASDM Launcher dialog box appears.

  3. If you have an enable password, but no actual users, skip the Username field, fill in the enable password in the Password field, and click OK.

    If you have already created an administrative user, provide the username and password in the appropriate fields.


     The Starting Point page appears.


    4. Select one of the following, based on whether you are setting up the ASA initially or    whether you are using setup to change an existing ASA installation:
  • Modify Existing Configuration: You can choose to modify the existing configuration.

  • Reset Configuration to Factory Defaults: With the exception of the management interface, modify the default configuration. As it turns out, a lot of small networks out there require only simple changes to their configuration, and as such, re-running the Start-up Wizard is the easiest way to make these changes.


 5. Click the Next button.

     The Basic Configuration page, appears with two optional items which you can choose to do.

 6. (Optional) Select from the following items:
  • Configure the Device for Teleworker Usage: This option supports teleworkers or remote workers via a virtual private network (VPN). If you select this option, you are presented with an extra page of questions for the Easy VPN Remote Configuration near the end of the Startup Wizard.

    On this page, you can also tell the Startup Wizard the name of the firewall device, such as ASAFirewall1, and the domain name to which the device belongs, such as edtetz.net.

  • Change Privileged Mode (Enable) Password: If you are not happy with your current enable password, change it here before you complete this step of the Start-up Wizard.
    
      11. Click the Next button. 
           The Interface IP Address Configuration page appears.
      12. Assign IP configuration for each of your IP addresses.
 
For your outside address, you can manually assign an address, which is not uncommon for business Internet connections. If your Internet connection supports either Dynamic Host Configuration Protocol (DHCP) or Point-to-Point Protocol over Ethernet (PPPOE), select the appropriate option.

If you use DHCP, tell your ASA to use the default gateway it receives from DHCP as the system-wide default gateway for this device. If you choose not to use the system-wide default gateway option, you need to configure a manual route through ASDM or the route outside 0 0 <IP address of gateway> at the command-line interface (CLI).


     13. Click the Next button.
 
           The DHCP Server page appears. For small businesses or regional offices, the ASA may represent the only real device on the network other than printers and computers. You may have these locations set up without any local servers onsite.

     14. (Optional) Select the Enable DHCP Server on the Inside Interface check box to have the ASA act as a DHCP server for this network segment.

     15. (Optional) Select the Enable Auto-Configuration from Interface check box so that you can copy most of these settings from an existing interface.

Enabling the Auto-Configuration check box is very useful for Domain Name System (DNS) and Windows Internet Name Service (WINS) server addresses that are constantly being used on all network segments and may all be the same for the organization.

     16. Configure or change any of the missing information in the following:
  • Starting IP Address: The first address to be handed out in the DHCP range.

  • Ending IP Address: The last address to be handed out in the DHCP range.

  • DNS servers 1 and 2: The DNS servers that are handed out to DHCP clients.

  • WINS servers 1 and 2: The WINS servers that are handed out to DHCP clients.

  • Lease Length: The lease length determines when DHCP clients are required to renew their leases on the DHCP supplied addresses.

  • Ping Timeout: The Ping Timeout setting is used by the DHCP server because it pings each address that it is ready to give, prior to assigning the address, to verify that the address is not in use. This reduces the chance of duplicate IP addresses being created on the network.

  • Domain Name: The domain name of the DHCP client belongs to.


       17. Click the Next button.

            The Address Translation (NAT/PAT) page appears.

      18. Set up Network Address Translation or Port Address Translation.
            Choose from the available address translation methods:
  • Use Port Address Translation (PAT): Most small offices, which use only one public IP address on their Internet connection, use PAT on their connection. PAT can use a specific address or the main address from their outside VLAN interfaces. PAT allows an entire office to share (or translate to) a single external IP address for Internet access.

  • Use Network Address Translation (NAT): Selecting NAT puts one-to-one mapping (or translation) between internal and external IP addresses, so you can specify a range of addresses to use on the outside VLAN interface.

    If you use ASA internally on your network (for example, to protect a server subnet), you may want to select the Enable Traffic through the Firewall Without Address Translation radio button if you use public addresses on your internal network (not likely) or if you use the ASA as firewall on the interior of your network.


      19. Click the Next button.
            
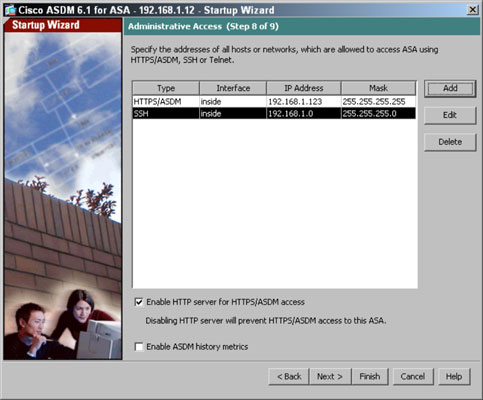
           The Administrative Access page appears.

      20. Set what systems on your network can connect to your ASA to perform management or configuration changes.
 
       Use the following process to add new management interfaces. If you want to use ASDM, you need to select the Enable HTTP Server for HTTPS/ASDM Access check box, whereas the Enable ASDM History Metrics check box saves usage data regarding accessing the ASDM interface.

       In the command line setup, you only have the option to ASDM connections to be made from a single computer. This page allows you to specify additional systems that can perform management of your ASA and the type of connection they make to perform that configuration.


If you add a new management option, the Add Administrative Access Entry dialog box appears. Select your desired options to create the new Administrative Access entry:
  1. Choose HTTP (ASDM), SSH, or Telnet from the Access Type drop-down list.

  2. Choose Inside from the Interface Name drop-down list.

    Inside is typically the most secure interface option, but in some cases, such as if you need to be able to conduct remote administration over the Outside interface, you should be very restrictive in the address from which the administration is performed.

  3. Specify either a specific address from which administration is performed in the IP Address text box or give a network range defined by either an IP address or a Network ID from the Subnet Mask drop-down list.

    Remember, the more restrictive you can be with this configuration, the more secure your ASA is.
  4. Click OK.

    You return to the Administrative Access page.
If you allow your firewall to be administered from the outside interface, you leave yourself open to potentially being compromised by someone you do not know.


      21. Click the Next button.
 
            The summary page of the configuration Start-up Wizard appears, providing a summary of the configuration that you have applied to the system. All these configuration changes are written into the running configuration on the ASA. After the configuration changes are made, you see the standard ASA ASDM management screen. From this interface you can
  • Perform any other configuration changes.

  • Relaunch the Startup Wizard or other wizards.

  • Perform basic monitoring of the ASA via the home page.

  • Perform more detailed monitoring of the ASA and connections that it hosts through the Monitoring pages.

  • Run additional management and troubleshooting tools.

  • Save the current configuration to flash memory.


BGP is a complex, advanced distance Exterior Gateway Protocol (EGP), BGP exchange routing information between Autonomous Systems ( - See more at: http://orbit-computer-solutions.com/BGP.php#sthash.4FLPX5lf.dpuf
BGP (Border Gateway Protocol)

Sunday, May 31, 2015

Calculate Input/Output Operations Per Second (IOPS) in a storage array

When it comes to measuring a storage system's overall performance, Input/Output Operations Per Second (IOPS) is still the most common metric in use. There are a number of factors that go into calculating the IOPS capability of an individual storage system.
In this article, I provide introductory information that goes into calculations that will help you figure out what your system can do. Specifically, I explain how individual storage components affect overall IOPS capability. I do not go into seriously convoluted mathematical formulas, but I do provide you with practical guidance and some formulas that might help you in your planning. Here are three notes to keep in mind when reading the article:
  • Published IOPS calculations aren't the end-all be-all of storage characteristics. Vendors often measure IOPS under only the best conditions, so it's up to you to verify the information and make sure the solution meets the needs of your environment.
  • IOPS calculations vary wildly based on the kind of workload being handled. In general, there are three performance categories related to IOPS: random performance, sequential performance, and a combination of the two, which is measured when you assess random and sequential performance at the same time.
  • The information presented here is intended to be very general and focuses primarily on random workloads.

IOPS calculations

Every disk in your storage system has a maximum theoretical IOPS value that is based on a formula. Disk performance -- and IOPS -- is based on three key factors:
  • Rotational speed (aka spindle speed). Measured in revolutions per minute (RPM), most disks you'll consider for enterprise storage rotate at speeds of 7,200, 10,000 or 15,000 RPM with the latter two being the most common. A higher rotational speed is associated with a higher performing disk. This value is not used directly in calculations, but it is highly important. The other three values depend heavily on the rotational speed, so I've included it for completeness.
  • Average latency. The time it takes for the sector of the disk being accessed to rotate into position under a read/write head.
  • Average seek time. The time (in ms) it takes for the hard drive's read/write head to position itself over the track being read or written. There are both read and write seek times; take the average of the two values.
To calculate the IOPS range, use this formula: Average IOPS: Divide 1 by the sum of the average latency in ms and the average seek time in ms (1 / (average latency in ms + average seek time in ms).

Sample drive:
  • Model: Western Digital VelociRaptor 2.5" SATA hard drive
  • Rotational speed: 10,000 RPM
  • Average latency: 3 ms (0.003 seconds)
  • Average seek time: 4.2 (r)/4.7 (w) = 4.45 ms (0.0045 seconds)
  • Calculated IOPS for this disk: 1/(0.003 + 0.0045) = about 133 IOPS
So, this sample drive can support about 133 IOPS. Compare this to the chart below, and you'll see that the value of 133 falls within the observed real-world performance exhibited by 10K RPM drives.
However, rather than working through a formula for your individual disks, there are a number of resources available that outline average observed IOPS values for a variety of different kinds of disks. For ease of calculation, use these values unless you think your own disks will vary greatly for some reason.
Below I list some of the values I've seen and used in my own environment for rough planning purposes. As you can see, the values for each kind of drive don't radically change from source to source.


 Note: The drive type doesn't enter into the equation at all. Sure, SAS disks will perform better than most SATA disks, but that's only because SAS disks are generally used for enterprise applications due to their often higher reliability as proven through their mean time between failure (MTBF) values. If a vendor decided to release a 15K RPM SATA disk with low latency and seek time values, it would have a high IOPS value, too.

Multidisk arrays

Enterprises don't install a single disk at a time, so the above calculations are pretty meaningless unless they can be translated to multidisk sets. Fortunately, it's easy to translate raw IOPS values from single disk to multiple disk implementations; it's a simple multiplication operation. For example, if you have ten 15K RPM disks, each with 175 IOPS capability, your disk system has 1,750 IOPS worth of performance capacity. But this is only if you opted for a RAID-0 or just a bunch of disks (JBOD) implementation. In the real world, RAID 0 is rarely used because the loss of a single disk in the array would result in the loss of all data in the array.
Let's explore what happens when you start looking at other RAID levels.

The IOPS RAID penalty

Perhaps the most important IOPS calculation component to understand lies in the realm of the write penalty associated with a number of RAID configurations. With the exception of RAID 0, which is simply an array of disks strung together to create a larger storage pool, RAID configurations rely on the fact that write operations actually result in multiple writes to the array. This characteristic is why different RAID configurations are suitable for different tasks.
For example, for each random write request, RAID 5 requires many disk operations, which has a significant impact on raw IOPS calculations. For general purposes, accept that RAID 5 writes require 4 IOPS per write operation. RAID 6's higher protection double fault tolerance is even worse in this regard, resulting in an "IO penalty" of 6 operations; in other words, plan on 6 IOPS for each random write operation. For read operations under RAID 5 and RAID 6, an IOPS is an IOPS; there is no negative performance or IOPS impact with read operations. Also, be aware that RAID 1 imposes a 2 to 1 IO penalty.
The chart below summarizes the read and write RAID penalties for the most common RAID levels.


Parity-based RAID systems also introduce other additional processing that result from the need to calculate parity information. The more parity protection you add to a system, the more processing overhead you incur. As you might expect, the overall imposed penalty is very dependent on the balance between read and write workloads.
A good starting point formula is below. This formula does not use the array IOPS value; it uses a workload IOPS value that you would derive on your own or by using some kind of calculation tool, such as the Exchange Server calculator.
(Total Workload IOPS * Percentage of workload that is read operations) + (Total Workload IOPS * Percentage of workload that is read operations * RAID IO Penalty)

As an example, let's assume the following:
  • Total IOPS need: 250 IOPS
  • Read workload: 50%
  • Write workload: 50%
  • RAID level: 6 (IO penalty of 6)
Result: You would need an array that could support 875 IOPS to support a 250 IOPS RAID 6-based workload that is 50% writes.
This could be an unpleasant surprise for some organizations, as it indicates that the number of disks might be more important than the size (i.e., you'd need twelve 7,200 RPM, seven 10K RPM, or five 15K RPM disks to support this IOPS need).

The transport choice

It's also important to understand what is not included in the raw numbers: the transport choice -- iSCSI or Fibre Channel. While the transport choice is an important consideration for many organizations, it doesn't directly impact the IOPS calculations. (None of the formulas consider the transport being used.)

The transport choice is an important one, but it's not the primary choice that many would make it out to be. For larger organizations that have significant transport needs (i.e., between the servers and the storage), Fibre Channel is a good choice, but this choice does not drive the IOPS wagon.

Summary

In order to intricately understand your IOPS needs, you need to know a whole lot, including specific disk technicalities, your workload breakdown as a function of read vs. write, and the RAID level you intend to use. Once you implement your solution, you can use tools that are tailor-made to IOPS analysis, such as Iometer, to get specific, real-time performance values. This assumes that you have a solution in place that you can measure.
If you're still in the planning stages or a deep level of analysis simply isn't necessary for your needs, the generalities presented in this article will help you figure out your needs.


Sources:

Saturday, May 23, 2015

NAT and PAT: A complete explanation

Network address translation (NAT) is the process of modifying IP address information in IP packet headers while in transit across a traffic routing device.
There are two different types of NAT:

NAT

    • Static NAT: The simplest type of NAT provides a one-to-one translation of IP addresses. It is often also referred to as one-to-one NAT. In this type of NAT only the IP addresses, IP header checksum and any higher level checksums that include the IP address need to be changed. The rest of the packet can be left untouched (at least for basic TCP/UDP functionality, some higher level protocols may need further translation). Basic NATs can be used when there is a requirement to interconnect two IP networks with incompatible addressing. With static NAT, translations exist in the NAT translation table as soon as you configure static NAT command(s), and they remain in the translation table until you delete the static NAT command(s).
    • Dynamic NAT: Dynamic NAT has some similarities and differences compared to static NAT. Like static NAT, the NAT router creates a one-to-one mapping between an inside local and inside global address and changes the IP addresses in packets as they exit and enter the inside network. However, the mapping of an inside local address to an inside global address happens dynamically. Dynamic NAT sets up a pool of possible inside global addresses and defines matching criteria to determine which inside local IP addresses should be translated with NAT. The dynamic entry stays in the table as long as traffic flows occasionally. With dynamic NAT, translations do not exist in the NAT table until the router receives traffic that requires translation. Dynamic translations have a timeout period after which they are purged from the translation table.
  •  

PAT

    • Static PAT: Static PAT translations allow a specific UDP or TCP port on a global address to be translated to a specific port on a local address. Static PAT is the same as static NAT, except that it enables you to specify the protocol (TCP or UDP) and port for the real and mapped addresses. Static PAT enables you to identify the same mapped address across many different static statements, provided that the port is different for each statement. You cannot use the same mapped address for multiple static NAT statements. With static PAT, translations exist in the NAT translation table as soon as you configure static PAT command(s), and they remain in the translation table until you delete the static PAT command(s).
    • NAT Overload or PAT: It is common to hide an entire IP address space, usually consisting of private IP addresses, behind a single IP address (or in some cases a small group of IP addresses) in another (usually public) address space. This type of NAT is called PAT in overload. The dynamic entry stays in the table as long as traffic flows occasionally. With PAT in overload, translations do not exist in the NAT table until the router receives traffic that requires translation. Translations have a timeout period after which they are purged from the translation table.

    Example #1: Static Source NAT

    How to translate the 172.16.0.5 IP address to the 10.16.0.5 ip address.


    Define the ip nat inside:

    Router(config)#interface fa0/0
    Router(config-if)#ip nat inside


     Define the ip nat outside:

    Router(config)#interface fa0/1
    Router(config-if)#ip nat outside

    Define the static NAT entry:

    ip nat inside source static 172.16.0.5 10.16.0.5
     
    With static NAT, translation exists in the NAT translation table as soon as you configure static NAT command, and it remains in the translation table until you delete the static NAT command:

    Router#sh ip nat translations
    Pro  Inside global      Inside local       Outside local      Outside global
    ---  10.16.0.5          172.16.0.5         ---                ---
    Router#

    If the client sends an ICMP packet or an HTTP request to the web server, the nat table will be:
     
    Router#sh ip nat translations
    Pro  Inside global      Inside local       Outside local      Outside global
    icmp 10.16.0.5:1        172.16.0.5:1       10.0.0.100:1       10.0.0.100:1
    tcp  10.16.0.5:56080    172.16.0.5:56080   10.0.0.100:80      10.0.0.100:80
    ---  10.16.0.5          172.16.0.5         ---                ---
    Router#

    Remember: Because the mapped address is the same for each consecutive connection with static NAT, and a persistent translation rule exists, static NAT allows hosts on the destination network to initiate traffic to a translated host (if an access list exists that allows it).

    Example #2: Dynamic Source NAT 

  •  How to translate the 172.16.0.0/28 network in the 10.16.0.0/29 network.

    Define the ip nat inside:

    Router(config)#interface fa0/0
    Router(config-if)#ip nat inside

    Define the ip nat outside:

    Router(config)#interface fa0/1
    Router(config-if)#ip nat outside
     
    Define the nat pool used in the NAT translation:

    Router(config)#ip nat pool dynamic-ip 10.0.16.1 10.0.16.6 prefix-length 29

    Define which network will be translated:

    Router(config)#ip access-list standard client-list
    Router(config-std-nacl)#permit 172.16.0.0 0.0.0.15

    Define the dynamic source NAT:
     
    Router(config)#ip nat inside source list client-list pool dynamic-ip

    With dynamic NAT, translations do not exist in the NAT table until the router receives traffic that requires translation.

    Router#sh ip nat translations
    Router#

    but when some packets match the ACL..
     
    Router#sh ip nat translations                              
    Pro Inside global      Inside local       Outside local      Outside global
    icmp 10.0.16.1:2       172.16.0.1:2       10.0.0.100:2       10.0.0.100:2
    tcp 10.0.16.2:35694    172.16.0.2:35694   10.0.0.100:80      10.0.0.100:80
    tcp 10.0.16.1:56185    172.16.0.1:56185   10.0.0.100:80      10.0.0.100:80
    --- 10.0.16.1          172.16.0.1         ---                ---
    --- 10.0.16.2          172.16.0.2         ---                ---
    Router#


     Note: If a new packet arrives from yet another inside host, and it needs a NAT entry, but all the pooled IP addresses are in use, the router simply discards the packet.
    This can be checked enabling the “debug ip nat”.

     May 12 19:26:09.895: NAT: translation failed (E), dropping packet s=172.16.0.5 d=10.0.0.100

    The user must try again until a NAT entry times out, at which point the NAT function works for the next host that sends a packet. Essentially, the inside global pool of addresses needs to be as large as the maximum number of concurrent hosts that need to use the Internet at the same time—unless we use PAT.

    Remember: The main difference between dynamic NAT and a range of addresses for static NAT is that static NAT allows a remote host to initiate a connection to a translated host (if an access list exists that allows it), while dynamic NAT does not. You also need an equal number of mapped addresses as real addresses with static NAT.

    Example #3: Static PAT

    How to expose two different services on Internet:
  • The Web server (172.16.0.5) is listening on tcp port 80; this server responds on public address 88.88.88.88:80 from the Internet (outside).
  • The SSH server (172.16.0.6) is listening on tcp port 22; this server responds on public address 88.88.88.88:666 from the Internet (outside)


  • Define the ip nat inside:

    Router(config)#interface fa0/0
    Router(config-if)#ip nat inside

    Define the ip nat outside:

    Router(config)#interface fa0/1
    Router(config-if)#ip nat outside

    Define the static PAT:
     The web server responds on tcp port 80 on the ‘outside’ interface.
     
    ip nat inside source static tcp 172.17.0.5 80 88.88.88.88 80

    The SSH server responds on tcp port 666 on the ‘outside’ interface ; in this case, the real port (22 tcp) is translated to the 666 tcp port when a request comes from Internet.
     
    ip nat inside source static tcp 172.17.0.6 22 88.88.88.88 666

    Like static NAT, static PAT translation exists in the NAT translation table as soon as you configure static PAT command, and it remains in the translation table until you delete the static PAT command.
     
    Router#sh ip nat translations 
    Pro Inside global      Inside local       Outside local      Outside global
    tcp 88.88.88.88:80     172.16.0.5:80      ---                ---
    tcp 88.88.88.88:666    172.16.0.6:22      ---                ---
    Router#

    If an Internet client sends an HTTP request or an SSH Connection (on tcp port 666), the nat table will be:
     
    Router#sh ip nat translations 
    Pro Inside global      Inside local       Outside local      Outside global
    tcp 88.88.88.88:80     172.16.0.5:80      56.56.56.56:54686  56.56.56.56:54686
    tcp 88.88.88.88:80     172.16.0.5:80      ---                ---
    tcp 88.88.88.88:666    172.16.0.6:22      56.56.56.56:33704  56.56.56.56:33704
    tcp 88.88.88.88:666    172.16.0.6:22      ---                ---
    Router#

     Example #4: PAT – NAT Overload

    How to share an Internet connection.


    Define the ip nat inside:

    Router(config)#interface fa0/0
    Router(config-if)#ip nat inside

    Define the ip nat outside:

    Router(config)#interface fa0/1
    Router(config-if)#ip nat outside

    Define which network will be translated:

    Router(config)#ip access-list standard client-list
    Router(config-std-nacl)#permit 172.16.0.0 0.0.0.255

    Define the NAT Overload:
     
    Router(config)#ip nat inside source list client-list interface fastethernet0/1 overload

    Like dynamic NAT, translations do not exist in the NAT table until the router receives traffic that requires translation:
     
    Router#sh ip nat translations
    Router#

    but when some packets match the ACL..
     
    Router#show ip nat translations
    Pro Inside global      Inside local       Outside local      Outside global
    tcp 88.88.88.88:7921   172.16.0.2:7921    95.100.96.233:443  95.100.96.233:443
    tcp 88.88.88.88:8651   172.16.0.5:8651    173.194.44.18:80   173.194.44.18:80
    tcp 88.88.88.88:8652   172.16.0.111:8652  173.194.44.18:443  173.194.44.18:443
    tcp 88.88.88.88:8653   172.16.0.223:8653  173.194.70.84:443  173.194.70.84:443
    udp 88.88.88.88:64116  172.16.0.222:64116 8.8.8.8:53         8.8.8.8:53
    udp 88.88.88.88:64756  172.16.0.223:64756 8.8.4.4:53         8.8.4.4:53
    Router#

     Other types of NAT/PAT


     One type of NAT/PAT widely used is the ip nat outside source; this command permits to translate the source address of a packet that enter in the ‘outside’ interface and leave the ‘inside’ interface.
    In simple terms, if you see the first example #1


    The command:

    ip nat outside source static 10.0.0.100 192.168.0.100

    translate the 10.0.0.100 to the 192.168.0.100 , so the client must call the 192.168.0.100 ip address to contact the server web and not the 10.0.0.100.
    Another particolar type of nat is the ip nat inside destination used when multiple inside devices are identical servers with mirrored content, which from the outside appear to be a single server load balancing.

    You define a pool of addresses containing the real hosts’ addresses ending with “type rotary” making the servers available in round-robin fashion. The access list now permits the IP address of the virtual host, i.e. what the outside world thinks is the host address. So the virtual host is 123.123.123.132, with the real hosts being 172.16.0.2 through 10.

    Partial configuration
     
    interface FastEthernet0/0
    ip address 172.16.0.0 255.255.255.0
    ip nat inside
    !
    interface FastEthernet0/1
    ip address 88.88.88.88 255.255.255.252
    ip nat outside
    !
    ip nat pool real-ip-server 172.16.0.2 172.16.0.10 prefix-length 24 type rotary
    ip nat inside destination list 1 pool real-ip-server
    !
    ip route 0.0.0.0 0.0.0.0 FastEthernet0/1
    !
    access-list 1 permit 123.123.123.123

    This translation is not bi-directional in nature. You will have to use a one to one static NAT to accomplish it. A “ip nat inside source static” kind of functionality can be achieved with the above configuration using a single address in the NAT pool, but that would only work for outside to inside traffic.


    Where apply nat inside/outside?


    Typically “ip nat inside” is configured on the interfaces in your local environment which cannot be routed to the Internet (typically private range of IP Addresses) and  and “ip nat outside” on the interface which is connected to the Internet.

     When does the router perform NAT? 


      Inside to Outside:

  • If IPSec then check input access list
  • decryption – for CET (Cisco Encryption Technology) or IPSec
  • check input access list
  • check input rate limits
  • input accounting
  • redirect to web cache
  • policy routing
  • routing
  • NAT inside to outside (local to global translation)
  • crypto (check map and mark for encryption)
  • check output access list
  • inspect (Context-based Access Control (CBAC))
  • TCP intercept
  • encryption
  • Queueing

Outside to Inside:

  1. If IPSec then check input access list
  2. decryption – for CET or IPSec
  3. check input access list
  4. check input rate limits
  5. input accounting
  6. redirect to web cache
  7. NAT outside to inside (global to local translation)
  8. policy routing
  9. routing
  10. crypto (check map and mark for encryption)
  11. check output access list
  12. inspect CBAC
  13. TCP intercept
  14. encryption
  15. Queueing

Some Useful Commands

  • To see some statistics about NAT: show ip nat statistics
  • To see a complete list of the static/dynamic NAT/PAT entries: show ip nat translations 
  • To clear dynamic nat entry: clear ip na translation *
  • To debug NAT: debug ip nat